Let's Encrypt: set up your free SSL certificate
Published on July 3, 2026 10 min read
Let's Encrypt issues free SSL certificates for https. Learn how it works, how automatic renewal works, and how to set it up in Plesk.

Let's Encrypt is a free, automated certificate authority that lets you secure your website with an SSL certificate. Visitors then reach your site over an encrypted https connection instead of unencrypted http. This article explains what Let's Encrypt is, how free SSL certificates work, how automatic renewal works, what LJPc arranges for you automatically and how to request a certificate yourself in Plesk.
What is Let's Encrypt?
Let's Encrypt is a certificate authority, or CA: an organisation that issues digital certificates so a website can offer its visitors an encrypted, trustworthy connection. What makes Let's Encrypt special is that it is entirely free of charge and fully automated.
Let's Encrypt is run by the non-profit ISRG (Internet Security Research Group). The service has been publicly available since 2015 and now secures hundreds of millions of websites. It is funded through donations and sponsorship, not through the sale of certificates.
Let's Encrypt only issues Domain Validated certificates, or DV for short. With a DV certificate, the CA checks that you control the domain, not who you are as an organisation. For almost any website, online shop or web application, that is all you need: a valid certificate and an encrypted connection. The difference with OV and EV certificates is explained in what an SSL certificate is.
How do free SSL certificates work?
An SSL certificate, technically a TLS certificate, does two things at once. It encrypts the traffic between your visitor's browser and your server, and it confirms that the visitor is genuinely connected to your domain. The browser shows that the connection is secure, and the web address starts with https.
The fact that a Let's Encrypt certificate is free says nothing about its quality. The encryption is as strong as with a paid certificate. The difference lies in what is checked and in extras such as Extended Validation or warranties, not in the security of the connection itself.
It is worth remembering what a DV certificate does not do. It secures the connection, but it is not a seal of approval for the company behind a website. A secure connection means the traffic is encrypted, not that the website is automatically trustworthy.
How does Let's Encrypt work? The ACME protocol
Let's Encrypt can only be free and work at scale because everything is automated. This is achieved with the ACME protocol (Automatic Certificate Management Environment). ACME is an open standard that lets software request a certificate, complete the validation and install the certificate without any human involvement.
To do this, an ACME client runs on your server. Well-known examples are Certbot and acme.sh, but control panels such as Plesk and cPanel also have an ACME client built in. At LJPc, that client is part of Plesk and our system requests the certificate for you automatically, so you do not have to install anything yourself.
Domain validation: HTTP-01 and DNS-01
Before Let's Encrypt issues a certificate, you have to prove that you control the domain. This is checked through a validation process, usually in one of these two ways:
- HTTP-01: the ACME client places a unique file at a fixed path on your web server. Let's Encrypt fetches that file to confirm that you control the server. The path looks like this:
http://yourdomain.com/.well-known/acme-challenge/<token>- DNS-01: you add a temporary TXT record to your DNS, under the name _acme-challenge. This method is required for wildcard certificates and also works when your server is not publicly reachable.
_acme-challenge.yourdomain.com. TXT "<validation-value>"For HTTP-01 validation, your domain has to point to your server's IP address through an A record, and through an AAAA record for IPv6 if you have one. If it does not, Let's Encrypt cannot run the validation and the request fails.
Validity and automatic renewal
A Let's Encrypt certificate is currently valid for 90 days. That short lifetime is a deliberate choice. It limits the damage if a key is ever leaked, and it pushes administrators to automate renewal.
Requesting a new certificate by hand every three months is awkward and error-prone. Renewal should therefore happen automatically. The ACME client keeps track of how long a certificate remains valid and renews it well in time. Plesk renews a Let's Encrypt certificate automatically 30 days before it expires, so after about two-thirds of its lifetime.
Certificate lifetimes will get shorter step by step over the coming years, not only at Let's Encrypt but across the whole industry. Let's Encrypt has announced that its default certificates will be valid for 64 days from 10 February 2027 and for 45 days from 16 February 2028. A new lifetime applies from the next renewal. On top of that, Let's Encrypt has offered six-day certificates on request since January 2026. That only makes automatic renewal more important. According to Let's Encrypt, most users who renew automatically do not need to change anything.
What LJPc arranges for you automatically
Every LJPc hosting package includes a free Let's Encrypt certificate, and usually you do not need to request it yourself. Every fifteen minutes our system checks which sites on your hosting package do not have a valid certificate yet and requests one through Plesk, for your domain and for the www version. It also turns on HSTS, a header that tells browsers to open your site over https only. After that, Plesk renews the certificate automatically.
Before our system requests a certificate, it checks that your domain and www.yourdomain.com point to your hosting package with their A record, and their AAAA record if there is one. We check this at Google, at Cloudflare and at your domain's nameservers, so the certificate is only requested once your DNS change is actually visible. Your CAA record must also allow Let's Encrypt. If your domain still points elsewhere, our system tries again every fifteen minutes. If your DNS is with another provider, the DNS check in Plesk shows which records are not right yet; how to open and read that check is explained in how to point a domain registered elsewhere to LJPc hosting. When everything is in place, you usually have a certificate within an hour. How long a DNS change takes to spread is explained in what DNS propagation is.
If the request itself fails, for example because Let's Encrypt could not complete its check, our system only tries again after seven days. If you do not want to wait that long, request the certificate yourself in Plesk as described below, or contact support.
Setting up Let's Encrypt yourself in Plesk
Do you want the certificate right away, do you still have no certificate after a few hours while your domain is set up correctly, or did an automatic request fail? Then request it yourself in Plesk. Plesk is in English by default, so we use the English names here.
- Log in to the customer portal, choose Services and then Sites in the menu, open your site and click Log in to Plesk in the Site overview block. You can read how that works in Open Plesk from the customer portal.
- You land on Websites & Domains. For your domain, click SSL/TLS Certificates in the Security block. The status is shown below the button, for example Domain not secured if there is no valid certificate yet.
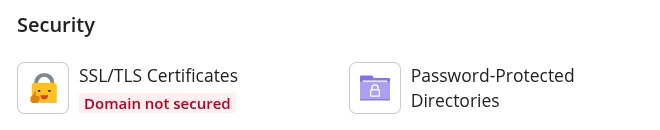
- Under Install a free basic certificate provided by Let's Encrypt, click Install.
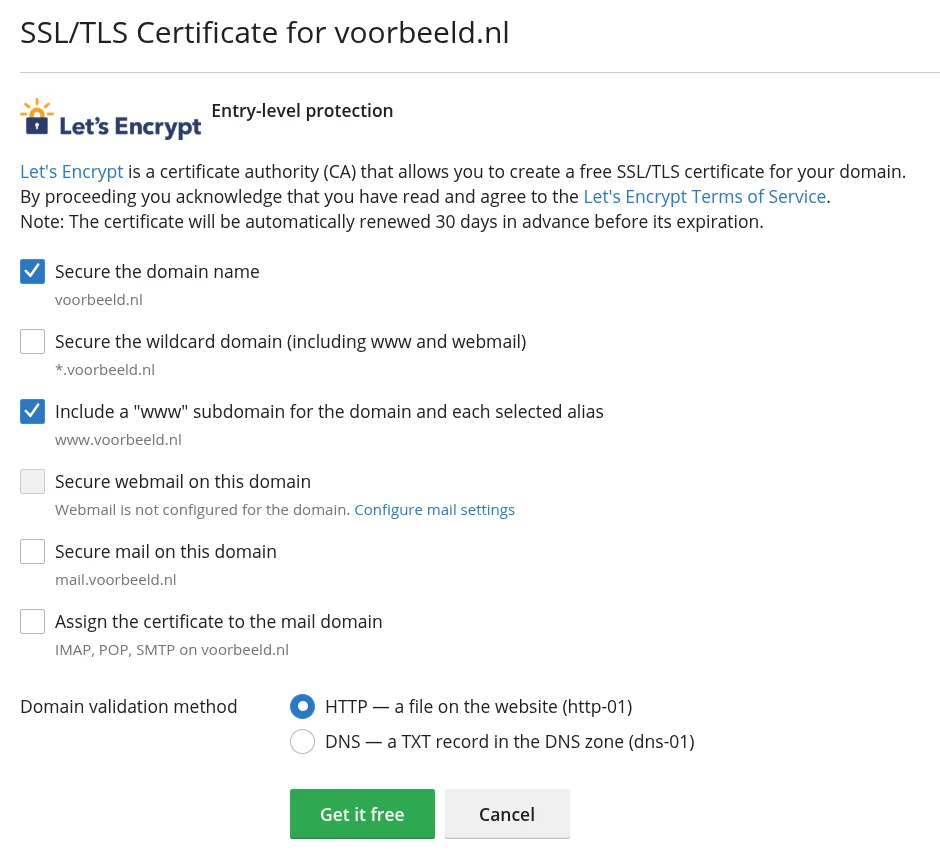
- In the window, keep Secure the domain name ticked and also tick Include a "www" subdomain for the domain and each selected alias. That box is not always ticked by default. Without it, a visitor on www.yourdomain.com gets a certificate error.
- Leave the other options off. You rarely need a wildcard (see below), and you do not need the mail and webmail options either: your mail program and your webmail connect to ljpc.email, which has its own certificate.
- Leave Domain validation method set to HTTP (http-01) and click Get it free. Plesk requests the certificate from Let's Encrypt and installs it straight away. It is usually active within a few minutes.
The redirect from http to https is on by default at LJPc: the option Permanent SEO-safe 301 redirect from HTTP to HTTPS under Hosting Settings of your domain. Test it by opening your domain with http:// in front: if you land on the https version, it works. You can read more about redirects in Set up .htaccess: redirects, security and more.
If you request the certificate yourself, HSTS is not turned on automatically. How to check whether HSTS is on and how to turn it on is explained in HTTP security headers. Under SSL/TLS Certificates you can also see when your certificate expires.
Wildcard certificate
If you want to secure all your subdomains at once with a single certificate, for example *.yourdomain.com, you need a wildcard certificate. Let's Encrypt issues these, but only through DNS-01 validation. At LJPc, every domain and every subdomain on your hosting package automatically gets its own free certificate, so a wildcard is rarely needed. If you want one anyway, contact support.
If your site works on yourdomain.com but www.yourdomain.com shows a certificate error, a wildcard will not fix it. Either the www record does not point to your hosting package yet, or the www option was off when the certificate was requested. Point the www record to your hosting package and then request the certificate again in Plesk with the www option ticked (see step 4 above). If a subdomain points to another provider's service with a CNAME record, for example a webshop platform, that provider takes care of the certificate for that subdomain.
Let's Encrypt and the CAA record
With a CAA record, you decide in your DNS which certificate authorities may issue a certificate for your domain. With an LJPc hosting package, letsencrypt.org is already in your CAA record by default, for your domain and for your subdomains. If you add another issuer yourself, keep letsencrypt.org next to it. The record looks like this:
yourdomain.com. CAA 0 issue "letsencrypt.org"If you have no CAA record, for example because your DNS is hosted elsewhere, any publicly trusted CA may issue a certificate, including Let's Encrypt, and the request succeeds. If your CAA record excludes Let's Encrypt, the request is refused and our system will not request a certificate automatically either.
Common problems
If setting up or renewing gets stuck, it is usually down to one of these causes:
| Problem | Cause | Solution |
|---|---|---|
| Validation fails (HTTP-01) | Your domain or www does not point to your hosting package, or an AAAA record still points to your old host. | Make sure the A record and any AAAA record of your domain and of www point to your LJPc hosting package. |
| Still no certificate after a few hours | Your DNS change is not visible everywhere yet, or an automatic request failed. Our system then only tries again after seven days. | Check your DNS and request the certificate yourself in Plesk, or contact support. |
| Certificate is not renewed | Your domain no longer points to your hosting package, so the renewal cannot complete. | Restore the A record (and any AAAA record). As soon as your domain points to LJPc again, our system requests a new certificate automatically. |
| Request refused | A CAA record does not allow Let's Encrypt. | Put letsencrypt.org back in your CAA record, next to any other issuer. |
| Wildcard does not work | A wildcard certificate requires DNS-01 validation. | Contact support. Separate subdomains do not need a wildcard: they get their own certificate automatically. |
| Browser still shows a warning | The site still loads parts over http (mixed content), or the redirect to https is off. | Load all images and scripts over https, see fix mixed content and HTTPS errors. Check under Hosting Settings that Permanent SEO-safe 301 redirect from HTTP to HTTPS is on. |
Can't work it out, or not sure whether your certificate is set up correctly? Contact our support team, and we will take a look with you.
Frequently asked questions
Is Let's Encrypt really free?
Yes. Let's Encrypt issues SSL certificates entirely free of charge. The service is run by the non-profit ISRG and funded through donations and sponsorship. With every LJPc hosting package, our system requests the certificate for you automatically.
How long is a Let's Encrypt certificate valid?
A Let's Encrypt certificate is currently valid for 90 days. Plesk renews it automatically 30 days before it expires, so you do not have to keep track of anything yourself. Let's Encrypt is shortening the lifetime to 64 days in February 2027 and to 45 days in February 2028, which makes automatic renewal even more important.
Do I have to renew a Let's Encrypt certificate manually?
No. Plesk renews the certificate automatically 30 days before it expires. If that fails, for example because your domain no longer points to your hosting package, our system requests a new certificate as soon as your domain is set up correctly again. You can also request it again yourself in Plesk.
What is the difference between Let's Encrypt and a paid SSL certificate?
The encryption is equally strong with both. Let's Encrypt issues Domain Validated certificates, which only check that you control the domain. Paid certificates can also verify your organisation's identity or offer a warranty. For most websites, a free Let's Encrypt certificate is enough.
Does Let's Encrypt support wildcard certificates?
Yes, but only through DNS-01 validation, which places a TXT record in your DNS. At LJPc, every domain and every subdomain on your hosting package automatically gets its own certificate, so you usually do not need a wildcard. If you want one anyway, contact support.
Do I have to change my CAA record for Let's Encrypt?
Usually not. With an LJPc hosting package, letsencrypt.org is already in your CAA record by default. If you add another issuer yourself, keep letsencrypt.org next to it. Without a CAA record, you do not have to do anything and the request succeeds.
Do I also need to tick the mail and webmail options in Plesk?
No. Your mail program and your webmail connect to ljpc.email, which has its own certificate. For your website, tick the domain and www.
Why do I not have a certificate yet?
Our system requests the certificate as soon as your domain and www point to your hosting package, and it checks this every fifteen minutes. If you changed your DNS a moment ago, it usually takes up to an hour. If a request failed, our system only tries again after seven days. In the meantime, request the certificate yourself in Plesk or contact support.